
What is Ansible?
Ansible is an automation tool for:
Configuring servers
Deploying applications
Managing users, packages, files
Orchestrating multi-machine tasks
It uses:
YAML for writing instructions (called playbooks)
SSH to connect to remote machines
Modules to perform tasks (apt, yum, copy, template, user, service, etc.)
No agents, no daemons — just SSH + Python on the remote.
If you’ve ever spent a late night SSH’d into three different servers, copy-pasting the same commands, praying you don’t break production… Ansible is the tool that removes that pain.
It’s simple, it’s powerful, and best of all — it works the way your brain already thinks about systems:
“Here’s how I want this server to look. Make it so.”
In this post, I’m going to walk you through Ansible from playbooks all the way to the advanced patterns that make infrastructure clean, predictable, and properly scalable. And I’ll keep it practical — no enterprise fluff, no theory for the sake of theory.
Just the stuff that makes your life easier.
Why Ansible Just… Works
Ansible uses:
SSH (so no agents or daemons everywhere)
YAML (so your ‘code’ reads like a shopping list)
Modules (so you don’t need messy bash scripts)
It connects to your servers, checks what’s needed, and makes them match your desired configuration — reliably and repeatably.
You describe state.
Ansible handles the how.
That’s what makes it different from scripting tools. And why it becomes addictive once you start using it properly.
Playbooks: Where Everything Begins
A playbook is simply a list of instructions written in YAML.
Example:
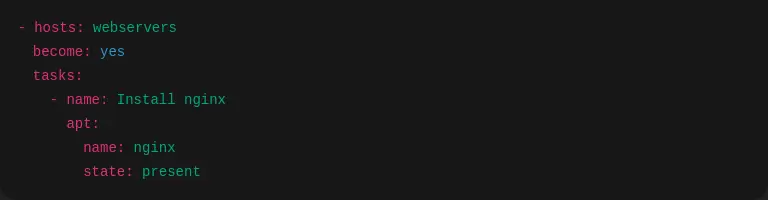
That’s the entire mental model:
define what you want → run the playbook → servers update themselves.
But once you go beyond a handful of tasks, things get messy…
…and that’s where roles come in.
Roles: The Secret to Clean, Reusable Automation
Roles are the difference between:
❌ One giant 600-line playbook
✔ Clean, maintainable, professional infrastructure code
A role has a predictable structure:
roles/
nginx/
tasks/
handlers/
templates/
files/
variables/
defaults/
This lets you break your infrastructure into logical, reusable chunks:
nginxphpmysqlSec-CorewordpressPrivate-Cloudetc.
Your playbooks become simple:
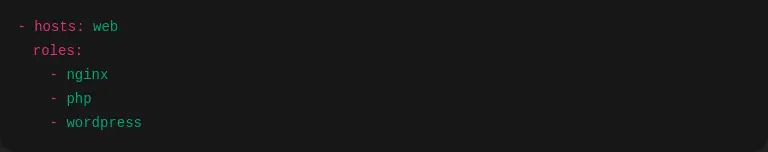
You can tell what the server does at a glance.
Best Practices (That Save You Hours Later)
1. Put user-configurable variables in defaults/, not vars/.
If it might change — put it in defaults so you can override it.
2. Template everything.
Skip the lineinfile hacks unless you must.
3. Keep tasks small and predictable.
One action = one task.
4. Notify handlers to reload services when configs change.
This avoids unnecessary restarts.
5. Don’t cram too much into one role.
One role = one job.
Modularity wins long-term.
Advanced Patterns That Make Ansible Feel Magic
Once you understand roles and variables, there’s a whole toolbox of features that make Ansible fast, flexible and production-ready.
Let’s hit the important ones.
Role Dependencies
Roles can depend on other roles — great for layered stacks.
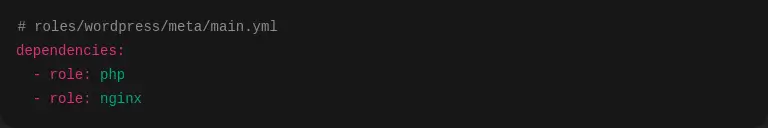
WordPress now always brings its prerequisites with it.
Dynamic Inventory
Instead of static lists of servers, Ansible can pull hosts from:
Proxmox
AWS
KVM
Netbox
API endpoints
Your own Python script
Perfect for environments where VMs come and go.
You can update your infrastructure automatically just by spinning up a new VM — Ansible discovers it.
Jinja2 Filters (Your New Best Friend)
Filters make templates powerful:
Use defaults:
{{ port | default(8080) }}Pick items from a list:
{{ services | selectattr('enabled', 'equalto', true) | list }}Generate random passwords:
{{ lookup('password', '/dev/null length=24') }}Build paths safely:
{{ '/etc/nginx' | path_join('sites-enabled') }}
Once you start using filters, your templates become beautifully dynamic.
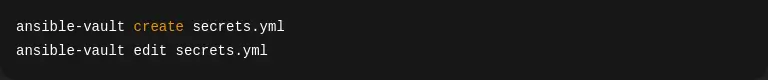
Ansible Vault (Keep Secrets Out of GitHub)
Never commit passwords or API keys.
Encrypt them:
Then include them safely:
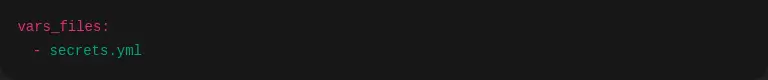
Simple. Secure.
Check Mode & Diff Mode
Before making changes, see what would change:
ansible-playbook site.yml --check
See file diffs:
--diff
Putting It All Together
A clean project might look like:
inventory/
group_vars/
host_vars/
roles/
nginx/
php/
mysql/
wordpress/
sec-core/
playbooks/
site.yml
Each role has:
sane defaults
small tasks
clean templates
handlers that only run when needed
Your infrastructure becomes stable, predictable, and painless to manage.
That’s the whole goal.
Ansible is one of those tools that rewards clarity.
The further you lean into roles, templates, and best practices, the smoother everything becomes.
It’s not just “automation” — it’s a living blueprint of your entire infrastructure, written in a way that future-you will understand instantly.