
Docker: What it is and what it does
If you’ve ever tried installing multiple apps on a server — NGINX here, MariaDB there, a Varnish proxy that won’t cooperate — you’ll know how quickly it can become a nightmare. Enter Docker. In this post, I’ll explain Docker step by step, in plain English.
What Docker Actually Is
At its core, Docker lets you run applications in containers — isolated environments that include everything the app needs: code, libraries, and settings. Unlike virtual machines, containers share your host OS kernel, so they’re small, fast, and start in seconds.
Think of it like this:
Images are frozen templates — the recipe.
Containers are running instances — the cooked meal.
Docker Engine is the chef — it pulls images, starts containers, manages networking and storage.
The key benefits:
“It works on my machine” problem solved – your app behaves the same wherever you run it.
Isolation – one container crashing won’t take down your entire system.
Repeatability & portability – rebuild stacks in seconds.
Ease of updates – stop, pull, start — no more “dependency hell.”
Docker vs KVM: When to Use Each
Before diving deeper, it’s worth comparing Docker with full virtual machines (KVM/QEMU that I’ve spoken about in an earlier post) — it’s another common way to self-host apps.
| Feature | Docker | KVM/QEMU (Virtual Machine) |
|---|---|---|
| Isolation | Process-level | Full OS |
| Startup time | < 1 second | 20–60 seconds |
| Resource usage | Low | High (full OS + memory) |
| Persistence | Volumes for data | Disk image (persistent by default) |
| Use case | Apps, services, microservices | Full OS, legacy apps, kernels, multiple OSes |
| Portability | Very portable (images) | Less portable (VM images) |
| Networking | Container networks, ports | Virtual NICs, bridges, full network stack |
When to use Docker:
Running apps like WordPress, Nextcloud, databases, or small services
Rapid deployment and reproducibility
Lightweight, low-overhead environments
When to use KVM:
You need a full OS (e.g., Ubuntu, Windows) with complete isolation
Running software that requires a specific kernel or OS version
Testing multiple OS setups or legacy applications
Practical takeaway:
Think of KVM as full virtual machines, great for heavyweight isolation or running multiple OSes. Docker is lightweight containers, perfect for apps and services that can share the host OS kernel.
Images and Containers: The Basics
An image is like a layered recipe:
ubuntu base → apt packages → nginx install → default config → entrypoint
When you run a container from an image:

Docker pulls the image (if you don’t have it)
Creates a writable container layer
Starts the app inside it
Visit http://localhost:8080, and you’re running a web server — without installing anything manually.
You can list containers with:
docker ps # running containers
docker ps -a # all containers
docker stop my-nginx
docker start my-nginx
docker rm my-nginx
Understanding this lifecycle — Created → Running → Exited → Removed — is crucial. It’s simple but powerful.
Persistent Data with Volumes
By default, containers are short-lived — once deleted, all data inside is gone. That’s no good for databases or configs. Enter volumes:
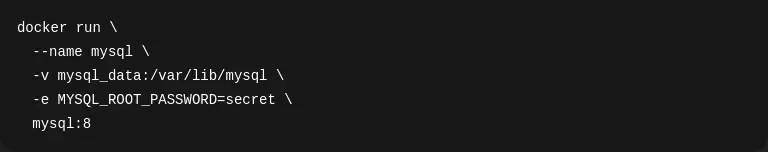
/var/lib/mysqlinside the container maps to a persistent Docker volume calledmysql_dataYour data survives restarts, upgrades, and container recreation
For dev work, you can also use bind mounts to link host folders to containers:
docker run -v /home/tim/nginx.conf:/etc/nginx/nginx.conf nginx
Networking Between Containers
Docker containers get their own network by default, but you can create custom networks so they talk to each other reliably:
docker network create webnet
docker run -d --name backend --network webnet containous/whoami
docker run -d --name frontend --network webnet containous/whoami
Inside this network, the backend container is reachable from frontend via http://backend.
This principle is critical for multi-container apps like WordPress + MariaDB or Private-Cloud + Redis + MariaDB.
Docker Compose: The Game Changer
Typing long ‘docker run' commands is fine for demos, but for real-world stacks, Docker Compose is a lifesaver. With a simple YAML file, you define:
Services
Images
Ports
Volumes
Networks
Dependencies
Example: a one-service stack:
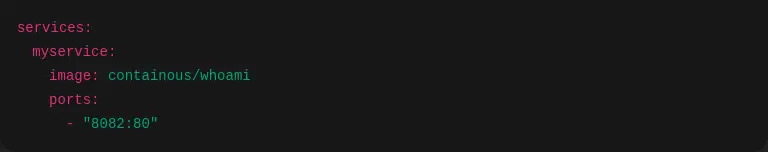
Run it with:
docker compose up -d
Stop it with:
docker compose down
It’s that simple.
For multi-container stacks, Compose automatically handles networking, making container-to-container communication as easy as referencing the container name.
Best Practices for Production-Ready Containers
Naming & Tagging:
Use meaningful names (nextcloud-db) and explicit image versions (nginx:1.25) instead of latest.
Volumes & Backups:
Persist database data in named volumes (dbdata). Backup regularly:
docker run --rm -v dbdata:/data -v $(pwd):/backup busybox tar cvf /backup/dbdata.tar /data
Networking Tips:
Use custom networks for multi-container stacks and avoid exposing databases publicly.
Environment Variables & Secrets:
Use .env files for passwords and sensitive info. Example:
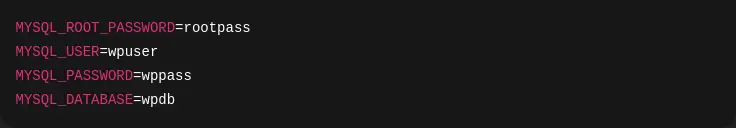
Updates & Maintenance:
Keep stacks fresh:
docker compose pull
docker compose up -d
docker system prune -a
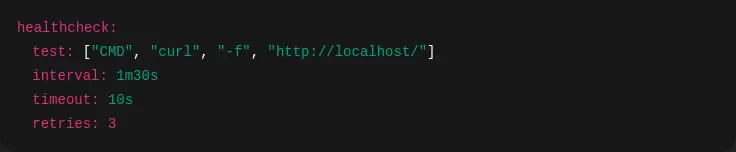
Logs & Healthchecks:
Inspect logs:
docker logs myservice
Add healthchecks in Compose:
There you have it, that’s Docker. We’ve covered:
The difference between images and containers
How volumes preserve data
How networks connect containers
How Compose makes stacks repeatable and maintainable
Best practices for real-world self-hosting
Docker might seem like magic at first, but it’s really just process isolation, persistence, and networking done smartly.
Time to set sail…Till next time.
Tim